
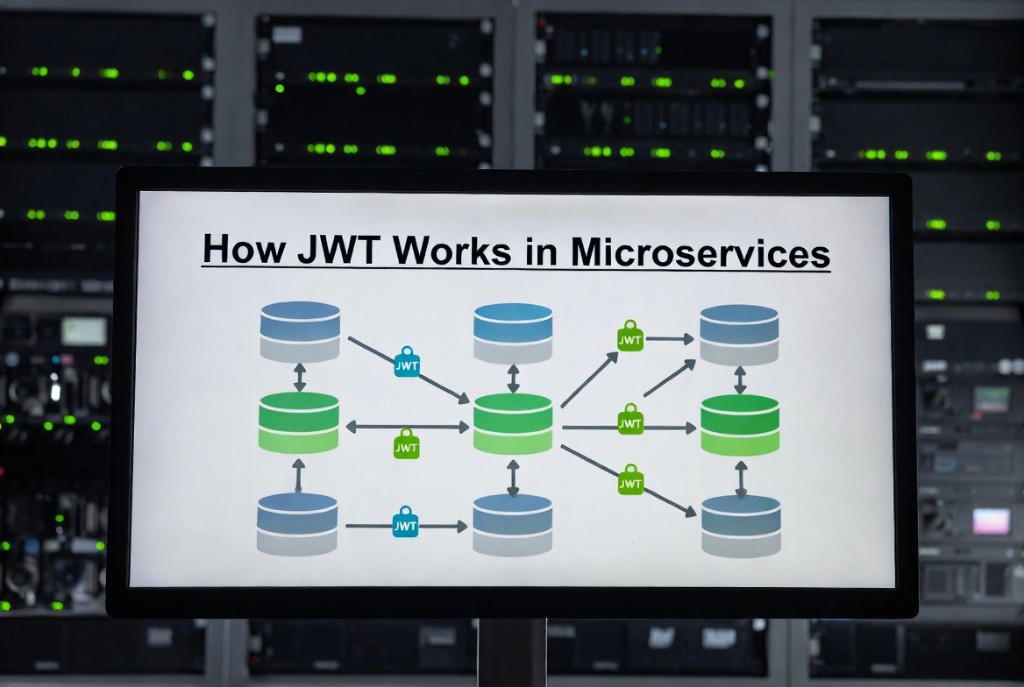
JWT in microservices
October 27, 2026 · 15 min read
Microservice meshes often treat the JWT as the portable identity artifact: validated once at the edge, forwarded internally, or exchanged for a service-specific credential. The failure mode is inconsistent verification - gateway checks signature while inner services trust headers anyone could forge.
Gateway validation at the edge
An API gateway or ingress controller validates JWT signature, exp, iss, and aud before routing. It may strip the Authorization header and inject trusted internal headers (X-User-Id) only after verification. Document that internal headers are not authentication on their own if they can be set by unvalidated paths.
- Fetch JWKS on a schedule; cache keys with kid matching.
- Reject tokens intended for another audience (
audmismatch). - Apply rate limits per subject and per IP at the gateway layer.
Passing JWT between services
Downstream HTTP calls can forward the original Bearer token when the callee needs end-user claims. gRPC metadata may carry the same string. Keep payloads small; prefer passing sub and scopes in signed internal tokens if the full JWT is huge or carries PII inner services do not need.
// Forward after gateway verified
const res = await fetch("http://orders/internal", {
  headers: { Authorization: `Bearer ${accessToken}` },
});
Service-to-service JWTs
Machine clients use client credentials JWTs with a service subject and narrow scopes. Do not reuse user access tokens for batch jobs. Rotate client secrets and use mTLS between nodes where possible in addition to JWT.
Claims for authorization inside the mesh
Map scope or custom roles claims to policy engines. Avoid embedding full permission tables in JWT - stale roles until expiry. For high-stakes actions, combine JWT with live permission lookup keyed by sub.
Debugging cross-service JWT failures
Trace IDs plus decoded jti help correlate 401s. Use the JWT decoder on tokens captured from staging; never paste production tokens into untrusted sites.
FAQ
- Should every microservice verify the JWT?
- Yes, unless you have a strict mTLS mesh where only verified gateways call services and you accept that risk model.
- Can I use the same JWT for all internal services?
- Only if aud/scopes cover all callees; otherwise issue service-specific tokens.
- What about synchronous chains timing out?
- Short exp reduces risk but increases refresh traffic; balance with gateway caching of introspection if using opaque tokens.
- How do meshes differ from gateways?
- Service meshes often use mTLS identities; JWT remains the user identity layer at HTTP boundaries.
Related: JWT authentication flow · JWT rate limiting · JWT best practices for APIs · Debug invalid JWT errors